


Tag: cybersecurity

Cyber systems and processes – strengthening the human link
The local business news cycle has taken a dark and repetitive turn. Week after week, headlines are dominated by a relentless spike in organisations falling victim to sophisticated hacks, data breaches, and crippling ransomware attacks. From local municipalities to major political parties like the ANC, no sector seems immune.

Fraud defence – do silos still work?
The Financial Sector Conduct Authority's (FSCA) call for a centralised anti-fraud hub at its 2026 conference reflects a timely recognition that South Africa's financial institutions (FIs) cannot successfully fight financial crime in isolation. However, centralisation alone is not enough.

Cyber-fraud in Africa is set to surge – are supply chains...
Cyber risk is no longer a peripheral IT issue in African supply chains. Instead, it is becoming a core operational threat. According to the Association of Chartered Certified Accountants (ACCA), 70% of organisations report experiencing fraud or economic crime. Cyber-enabled fraud ranks among the fastest-growing categories globally, according to the ACCA Global Economic Crime and Fraud Survey.

Cybersecurity as an exercise in risk tolerance
South African businesses have evolved alongside the reality of the country’s physical infrastructure challenges. Organisations instinctively build redundancies for power. These include solar installations, battery backup solutions, UPS systems and generators. When the grid fails, the failover system kicks in. Similarly, most businesses have multiple connectivity failovers because they understand operational disruption intimately.
Technology value, governance and optimisation – the Microsoft 365 case
Microsoft 365 is embedded in a significant number of South African organisations, but adoption doesn’t mean value. The difference between the two is showing up as cost and risk. There’s a reason companies invest in technology. It should deliver measurable gains across key areas such as productivity, cost and time savings, and operational optimisation.
Why prompt injection is becoming the new phishing
In biology, a virus does not always destroy a cell from the outside. Instead, it injects genetic instructions into the host. It then hijacks the cell’s internal machinery. This process produces more viruses. In the digital world, prompt injection follows a similar logic. It operates with stealth and precision.

SME cybersecurity – turning David’s compliance to a Goliath advantage
The enterprise Goliath is worried about its suppliers. These Small and Medium-sized Enterprises (SMEs) are underprepared. They are also disproportionately targeted. In fact, 43% of cyber-attacks target their digital front door. In addition, the Protection of Personal Information Act (POPIA) holds large organisations legally responsible when a supplier is breached.

Boards are underestimating the AI agent risk
Artificial Intelligence (AI) is rapidly moving from experimentation to execution within South African organisations. Organisations increasingly embed AI agents across business functions, including finance, customer service, IT and operations. However, a significant governance concern is emerging.
Credential abuse techniques – the tactics defenders still miss
According to our recent global report, password guessing and valid account misuse rank among the most effective tactics cyber criminals use in 2025. This trend reflects a strategic shift. Attackers now move away from noisy malware that triggers endpoint protection. Instead, they leverage legitimate access to evade detection.
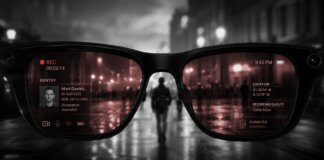
Surveillance, Privacy and Consent – smart glasses raise the risks
EssilorLuxottica and Meta sold more than seven million Ray-Ban and Oakley-branded smart glasses in 2025. Sales of these intelligent wearables increased almost threefold compared with 2023. As a result, the category moved into the mainstream.